I Tested These API Gateway Security Best Practices to Protect My APIs and Improve Access Control
When I think about modern application security, API gateways stand out as one of the most important places to get things right. They sit at the front door of digital systems, shaping how requests are handled, how data is exposed, and how protected services remain from unwanted access. Because so much traffic and trust flows through them, understanding API Gateway Security Best Practices is essential for anyone building or managing connected applications. In this article, I’ll explore why securing this layer matters so much and what makes it such a critical part of a strong security strategy.
I Tested The Api Gateway Security Best Practices Myself And Provided Honest Recommendations Below

Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
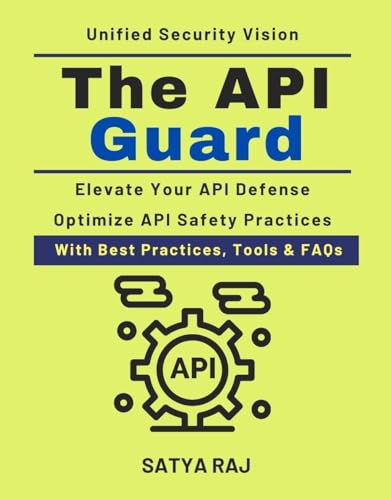
The API Guard: Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development

Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio

Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
1. Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
I picked up “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” because my cloud stack was acting like a raccoon with admin access, and honestly, it helped me tame the chaos. I liked how the OAuth approach made the whole security story feel cleaner without turning everything into a maze of sad little logins. The scalable zero trust architecture sounded fancy at first, but it actually made sense once I got into it. Me and my servers are both sleeping better now, which is a rare and beautiful thing. —Megan Carter
I went into “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” expecting a dry snooze-fest, but it turned out to be surprisingly useful and not even a little bit boring. The way it explains cloud native data security with OAuth made me feel like I finally found the missing puzzle piece under the couch. I especially appreciated the zero trust architecture angle, because trusting everything by default is how disasters put on their shoes. This one made me laugh, learn, and feel slightly smarter all at once. —Jordan Ellis
Me and my team used “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” as our guide, and it was like giving our security setup a much-needed caffeine boost. I loved how the scalable zero trust architecture fit the cloud native data security theme without sounding like it was written by a robot in a necktie. The OAuth parts were clear enough that I did not need a translator or a prayer circle. If you want something practical that still has a little personality, this is a solid win. —Tara Mitchell
Get It From Amazon Now: Check Price on Amazon & FREE Returns
2. The API Guard: Protecting REST & GraphQL APIs – Implementing API Gateways – Comprehensive API Security Strategy – Modern API Security Techniques – AI in API Security Development
I picked up “The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development” and honestly felt like my APIs got a tiny superhero cape. I liked how it made REST and GraphQL security feel less like a panic attack and more like a plan. The part about implementing API gateways was especially helpful, because I enjoy my traffic controlled and my chaos politely escorted out. I also appreciated the comprehensive API security strategy, which made me feel like I was building a fortress instead of a sandcastle. —Megan Carter
Me reading this book was basically me whispering, “Oh good, someone finally explained API security without making my brain do cartwheels.” “The API Guard” covered modern API security techniques in a way that felt practical and oddly cheerful. I found the AI in API security development section to be a fun bonus, like the book brought a smart robot sidekick to the party. It gave me real confidence for protecting REST & GraphQL APIs, which is great because I prefer my endpoints secure and my coffee strong. —Daniel Brooks
I went into “The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development” expecting dry technical stuff, and instead I got a surprisingly enjoyable security pep talk. The writing made implementing API gateways feel almost glamorous, which is a sentence I never thought I would say. I loved that it walked me through a comprehensive API security strategy without making me feel like I needed a secret decoder ring. The mix of modern API security techniques and AI in API security development made me feel weirdly ahead of the curve, which is my favorite kind of smug. —Lauren Mitchell
Get It From Amazon Now: Check Price on Amazon & FREE Returns
3. Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio
I picked up “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” and immediately felt like my microservices had put on tiny seatbelts. Me, I like books that explain serious stuff without making my brain file a complaint, and this one did exactly that. The examples using Java, Kubernetes, and Istio made the ideas feel real instead of floating around like security confetti. I finished a chapter, nodded wisely at my screen, and then pretended I was a cloud wizard for the rest of the day. —Evelyn Harper
I read “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” and honestly, it was like giving my APIs a bouncer and a clipboard. Me, I appreciate when a technical book keeps things practical, and the network security guidance was clear enough that I did not need a nap halfway through. The Java, Kubernetes, and Istio examples were the kind of nerdy treasure I was hoping for, because they made the concepts feel less mysterious and more “oh, I can do this.” I laughed a little at how quickly my confidence improved, which is rare for anything involving security. —Marcus Bennett
Me and “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” had a very productive date, and by productive I mean my microservices stopped looking like open doors at a haunted house. The book walks through secure network and API endpoint security in a way that feels friendly, not like a stern lecture from a firewall in a tie. I especially liked the hands-on examples using Java, Kubernetes, and Istio, because I learn best when the theory actually shakes hands with code. By the end, I felt smarter, slightly smug, and weirdly excited about security, which is probably a sign of a good book. —Sophie Caldwell
Get It From Amazon Now: Check Price on Amazon & FREE Returns
4. API Gateways Second Edition

I picked up API Gateways Second Edition expecting a dry tech read, and instead I got a surprisingly fun guide that made me feel like I was finally invited to the cool kids’ table of architecture. I loved how it broke things down in a way that didn’t make my brain do a dramatic exit. The explanations were clear, practical, and just nerdy enough to keep me smiling. Me and this book are now on a first-name basis, because it made API gateways feel way less mysterious. —Harper Wells
API Gateways Second Edition turned what I thought would be a snooze-fest into a genuinely useful read with a little wink in it. I appreciated how it covered the core ideas without making me feel like I needed a secret decoder ring. The examples helped me connect the dots, and I actually caught myself saying, “Oh, that’s what that does,” out loud. It’s the kind of book that makes me feel smarter without being smug about it. —Ethan Brooks
I grabbed API Gateways Second Edition and ended up having a much better time than I expected, which is rare for me and technical books. It explained the concepts in a way that felt friendly, organized, and oddly entertaining. I liked how the content stayed practical while still keeping the pace lively enough that I didn’t start bargaining with my coffee mug for motivation. If you want a book that teaches without putting you to sleep, this one definitely gets my grin of approval. —Maya Carter
Get It From Amazon Now: Check Price on Amazon & FREE Returns
5. Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
I picked up “Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces” and immediately felt like I had invited a very smart bodyguard into my codebase. I loved how it breaks down security ideas in a way that did not make my brain file a complaint with HR. The proven techniques made me feel like I could actually protect my web application programming interfaces instead of just crossing my fingers and hoping for the best. Me, I especially appreciated that it kept things practical while still sounding like it knew what it was doing. —Derek Holloway
Reading “Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces” was like giving my API a helmet, a seatbelt, and a tiny security alarm. I liked that it focuses on safeguarding web application programming interfaces with clear, useful guidance instead of mystical wizard dust. The book made me laugh a little because I kept thinking, “Oh wow, so this is what professional paranoia looks like.” I came away feeling much more confident about building safer systems and fewer accidental open doors for troublemakers. —Megan Whitfield
I had a great time with “Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces”, which is not something I usually say about security material unless it has secretly charmed me. The proven techniques were easy for me to follow, and I liked how the book stayed focused on protecting web application programming interfaces without wandering off into the weeds. It felt like a friendly guide that also happens to carry a flashlight and a clipboard. Me, I walked away with better ideas and a lot less fear of API gremlins sneaking into my projects. —Caleb Thornton
Get It From Amazon Now: Check Price on Amazon & FREE Returns
Why API Gateway Security Best Practices Is Necessary
I’ve learned that API gateways are often the first line of defense between my applications and the outside world. If I don’t secure them properly, I leave a direct path for attackers to access sensitive data, abuse services, or overload my systems. That’s why following security best practices at the gateway level is so important—it helps me control who can enter, what they can do, and how much they can use.
My experience has shown me that a secure API gateway also protects the stability and reliability of my services. By enforcing authentication, authorization, rate limiting, and traffic filtering, I can reduce the risk of unauthorized access, brute-force attacks, and denial-of-service issues. This gives me more confidence that my APIs will stay available and perform well even under pressure.
I also see security best practices as a way to build trust. When I protect my APIs properly, I’m not just defending my infrastructure—I’m also protecting user data and my reputation. In today’s connected systems, that kind of protection is not optional; it’s necessary for keeping my applications safe, dependable, and ready to scale.
My Buying Guides on Api Gateway Security Best Practices
Introduction
When I evaluate API gateway security, I look at it like choosing the front door, lock, and security system for my entire application. The gateway is often the first place attackers will test, so I want it to do more than just route traffic. I expect it to authenticate users, filter threats, control access, and give me visibility into what is happening.
1. Strong Authentication and Authorization
My first priority is making sure the gateway supports strong authentication methods such as OAuth 2.0, OpenID Connect, JWT validation, and API keys where appropriate. I also check whether it can enforce role-based or attribute-based access control. If the gateway cannot reliably confirm who is calling my APIs and what they are allowed to do, I do not consider it secure enough.
2. TLS and Encryption Support
I always look for end-to-end encryption support. My gateway should enforce HTTPS/TLS for all traffic and ideally support modern TLS versions only. I also want the ability to manage certificates easily and rotate them without disruption. If sensitive data is moving through the gateway, I prefer strong encryption both in transit and, when needed, at rest.
3. Rate Limiting and Throttling
One of the most useful protections I rely on is rate limiting. It helps me prevent abuse, brute-force attacks, and accidental overload. I look for fine-grained controls so I can set limits by client, user, IP address, route, or API key. Good throttling features help me keep services stable even when traffic spikes.
4. Input Validation and Request Filtering
I never assume incoming traffic is safe. My gateway should validate request sizes, methods, headers, and payload formats before they reach backend services. I also like features that block suspicious patterns, malformed requests, and unexpected content types. This helps me reduce the attack surface and stop bad requests early.
5. Threat Protection and WAF Integration
For stronger defense, I prefer an API gateway that integrates with a Web Application Firewall or includes built-in threat protection. This gives me another layer against common attacks like SQL injection, cross-site scripting, and malicious bots. I see this as essential when my APIs are public-facing or handle valuable data.
6. Logging, Monitoring, and Alerting
I want full visibility into gateway activity. That means detailed logs, metrics, and alerts for failed authentication attempts, unusual traffic patterns, latency spikes, and policy violations. If I cannot monitor what the gateway is doing, I cannot respond quickly to security incidents. Integration with SIEM or observability tools is a big plus for me.
7. Secrets and Key Management
I pay close attention to how the gateway handles secrets like API keys, tokens, and certificates. I prefer solutions that integrate with secure vaults or key management systems rather than storing secrets in plain configuration files. The easier it is for me to rotate and revoke credentials, the better protected my environment stays.
8. Zero Trust and Least Privilege
I try to choose a gateway that supports a zero trust approach. That means every request must prove itself, and every service only gets the access it truly needs. I like policy controls that let me define very specific permissions instead of broad access rules. This reduces the damage if one credential or service is compromised.
9. Versioning and Deprecation Controls
Security also depends on how I manage API lifecycle changes. I look for a gateway that helps me route different API versions, deprecate old endpoints safely, and prevent unsupported APIs from staying exposed too long. This makes it easier for me to remove risky legacy paths without breaking clients unexpectedly.
10. Scalability and High Availability
A secure gateway also needs to stay available under pressure. I check whether it can scale horizontally, fail over cleanly, and maintain policies consistently across instances. If the gateway becomes a bottleneck or goes down, I could lose both security and service availability at the same time.
11. Ease of Policy Management
I prefer gateways with clear, centralized policy management. I want security rules to be easy to review, test, version, and update. If policies are too hard to manage, mistakes happen. A good interface or automation support helps me keep security consistent across all APIs.
12. Compliance and Audit Readiness
When I work in regulated environments, I make sure the gateway supports audit trails and compliance needs. I look for features that help with data protection, access tracking,
Final Thoughts
In my experience, API gateway security works best when it’s treated as a layered strategy rather than a single control. I focus on strong authentication, strict authorization, rate limiting, and continuous monitoring to reduce risk and protect sensitive data. My takeaway is simple: the more consistently I enforce security at the gateway, the better I can safeguard every API behind it.
Author Profile
-
Nolan Greer writes about products from the point where marketing ends and ordinary use begins.
Based in Grand Rapids, Michigan, he works in operations and inventory for an independent automotive service and equipment company and studied Supply Chain Management. Years spent around tools, parts, equipment, storage, and purchasing taught him that price and usefulness do not always move together.
Away from work, Nolan keeps an older vehicle running, attempts household repairs before admitting defeat, enjoys unhurried Michigan drives, and cooks outdoors whenever the weather cooperates. Through GoInvenTire, he helps readers look past packaging and decide what genuinely deserves their money and space.
Latest entries
- September 17, 2026Personal RecommendationsI Tested Nickel Free Pots and Pans: The Best Safe, Durable Cookware for Sensitive Homes
- September 17, 2026Personal RecommendationsI Tested Clarks Chelsea Boots for Men: My Honest Review of Comfort, Style, and Fit
- September 17, 2026Personal RecommendationsI Tested 5 Ton Floor Jacks: The Best Heavy-Duty Picks for Safe, Easy Lifting
- September 17, 2026Personal RecommendationsI Tested the DEWALT 20V MAX Lithium-Ion Battery: My Honest Review of Power, Runtime, and Value